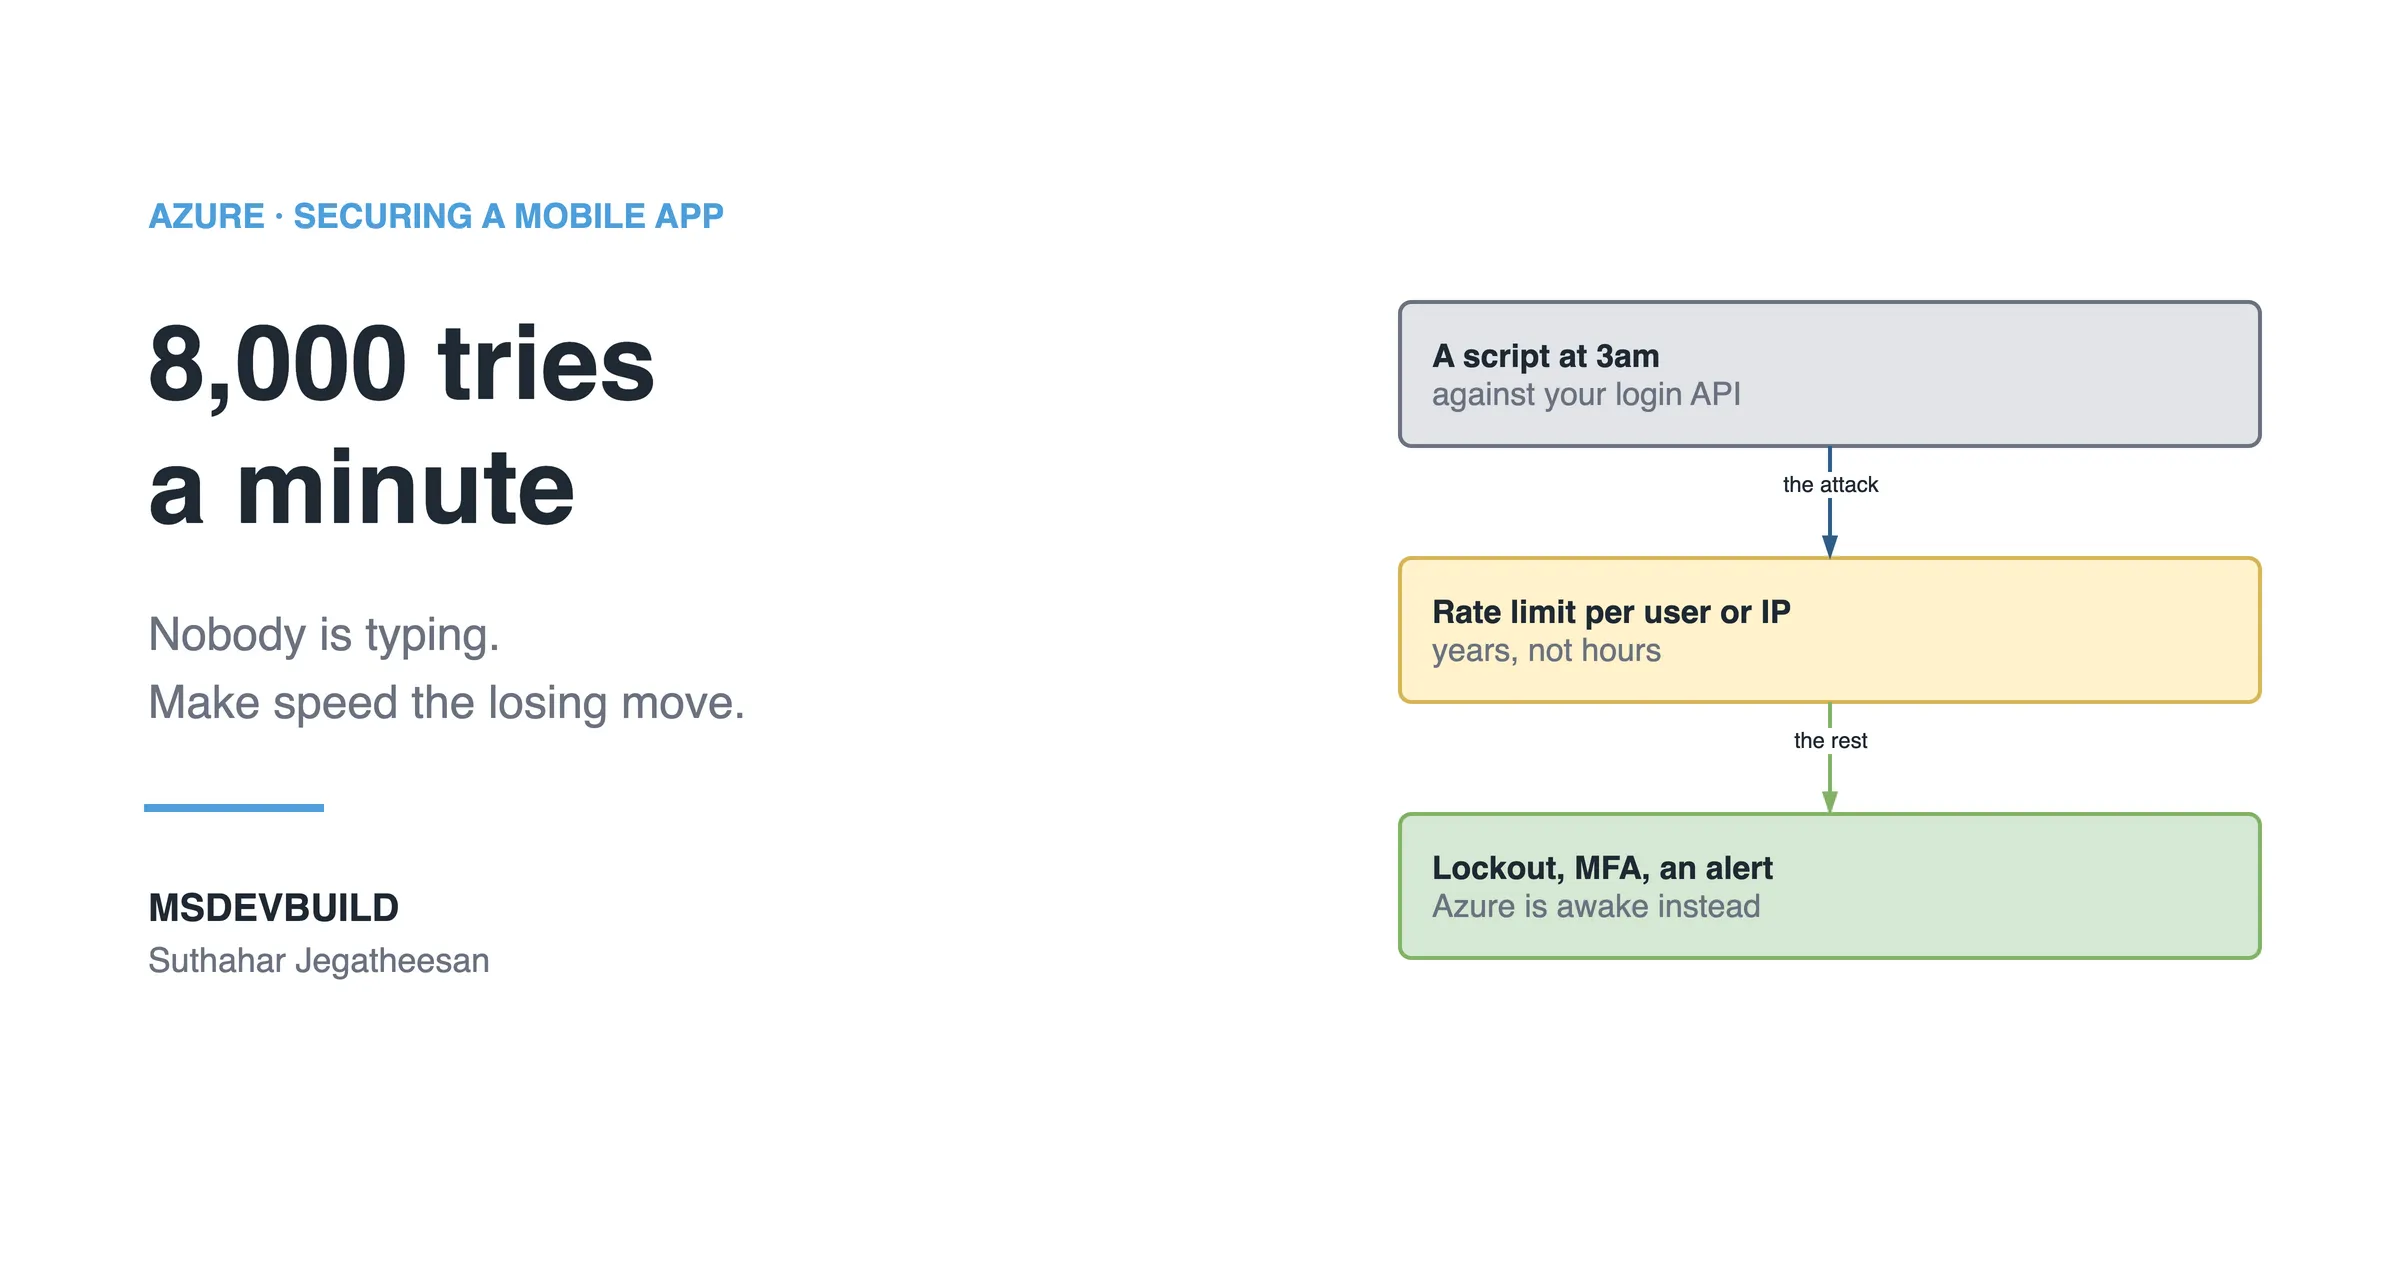
AI Bot Attacks on a Mobile App Login, and How Azure Stops Them
A script tries 8,000 passwords a minute against your login API at 3am. Rate limiting, smart lockout and Defender for Cloud make speed the losing move.
9 articles
A script tries 8,000 passwords a minute against your login API at 3am. Rate limiting, smart lockout and Defender for Cloud make speed the losing move.
Moving every secret into Key Vault leaves exactly one behind: the credential that opens the vault. A managed identity is what removes it.
HTTPS only, authentication, authorization, secrets and monitoring: five steps to secure a mobile API on Azure, and why the order carries most of the value.
How hotel booking confirmation works after payment: authorize, book with the supplier, then capture, and what happens if another site sells the room first.
When to use Azure Managed Redis, which replaces Azure Cache for Redis, learned from a flash sale that hit Azure SQL 2,200 times a second.
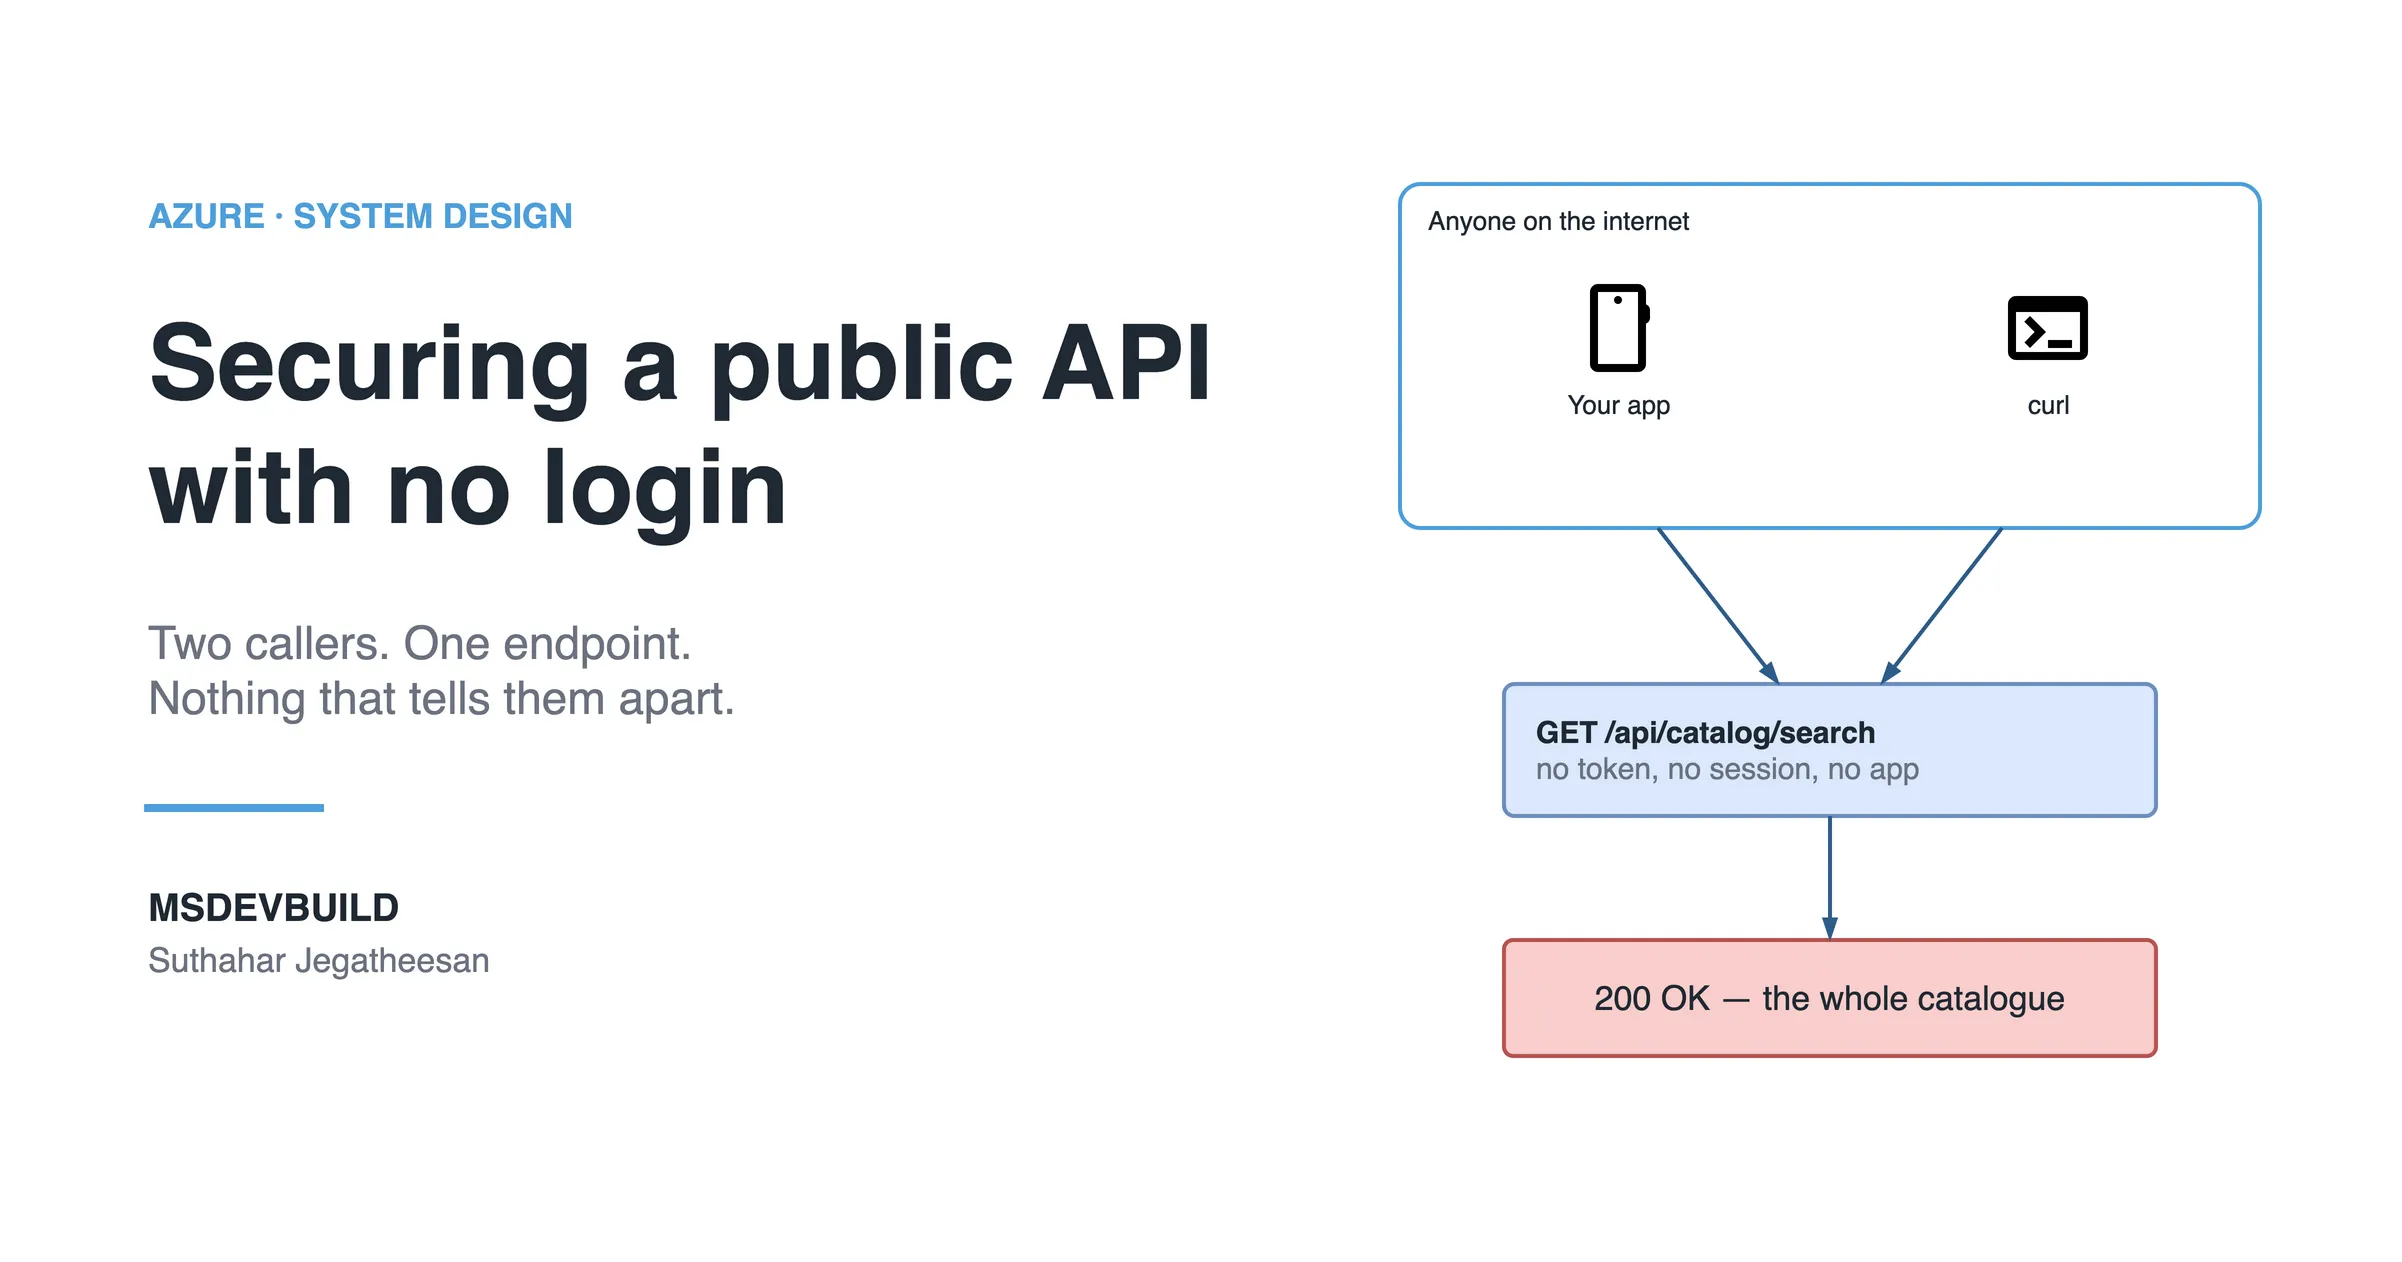
Browsing products without login was a real requirement. Trusting requests because they came from our own app was the bug, and curl does not care.
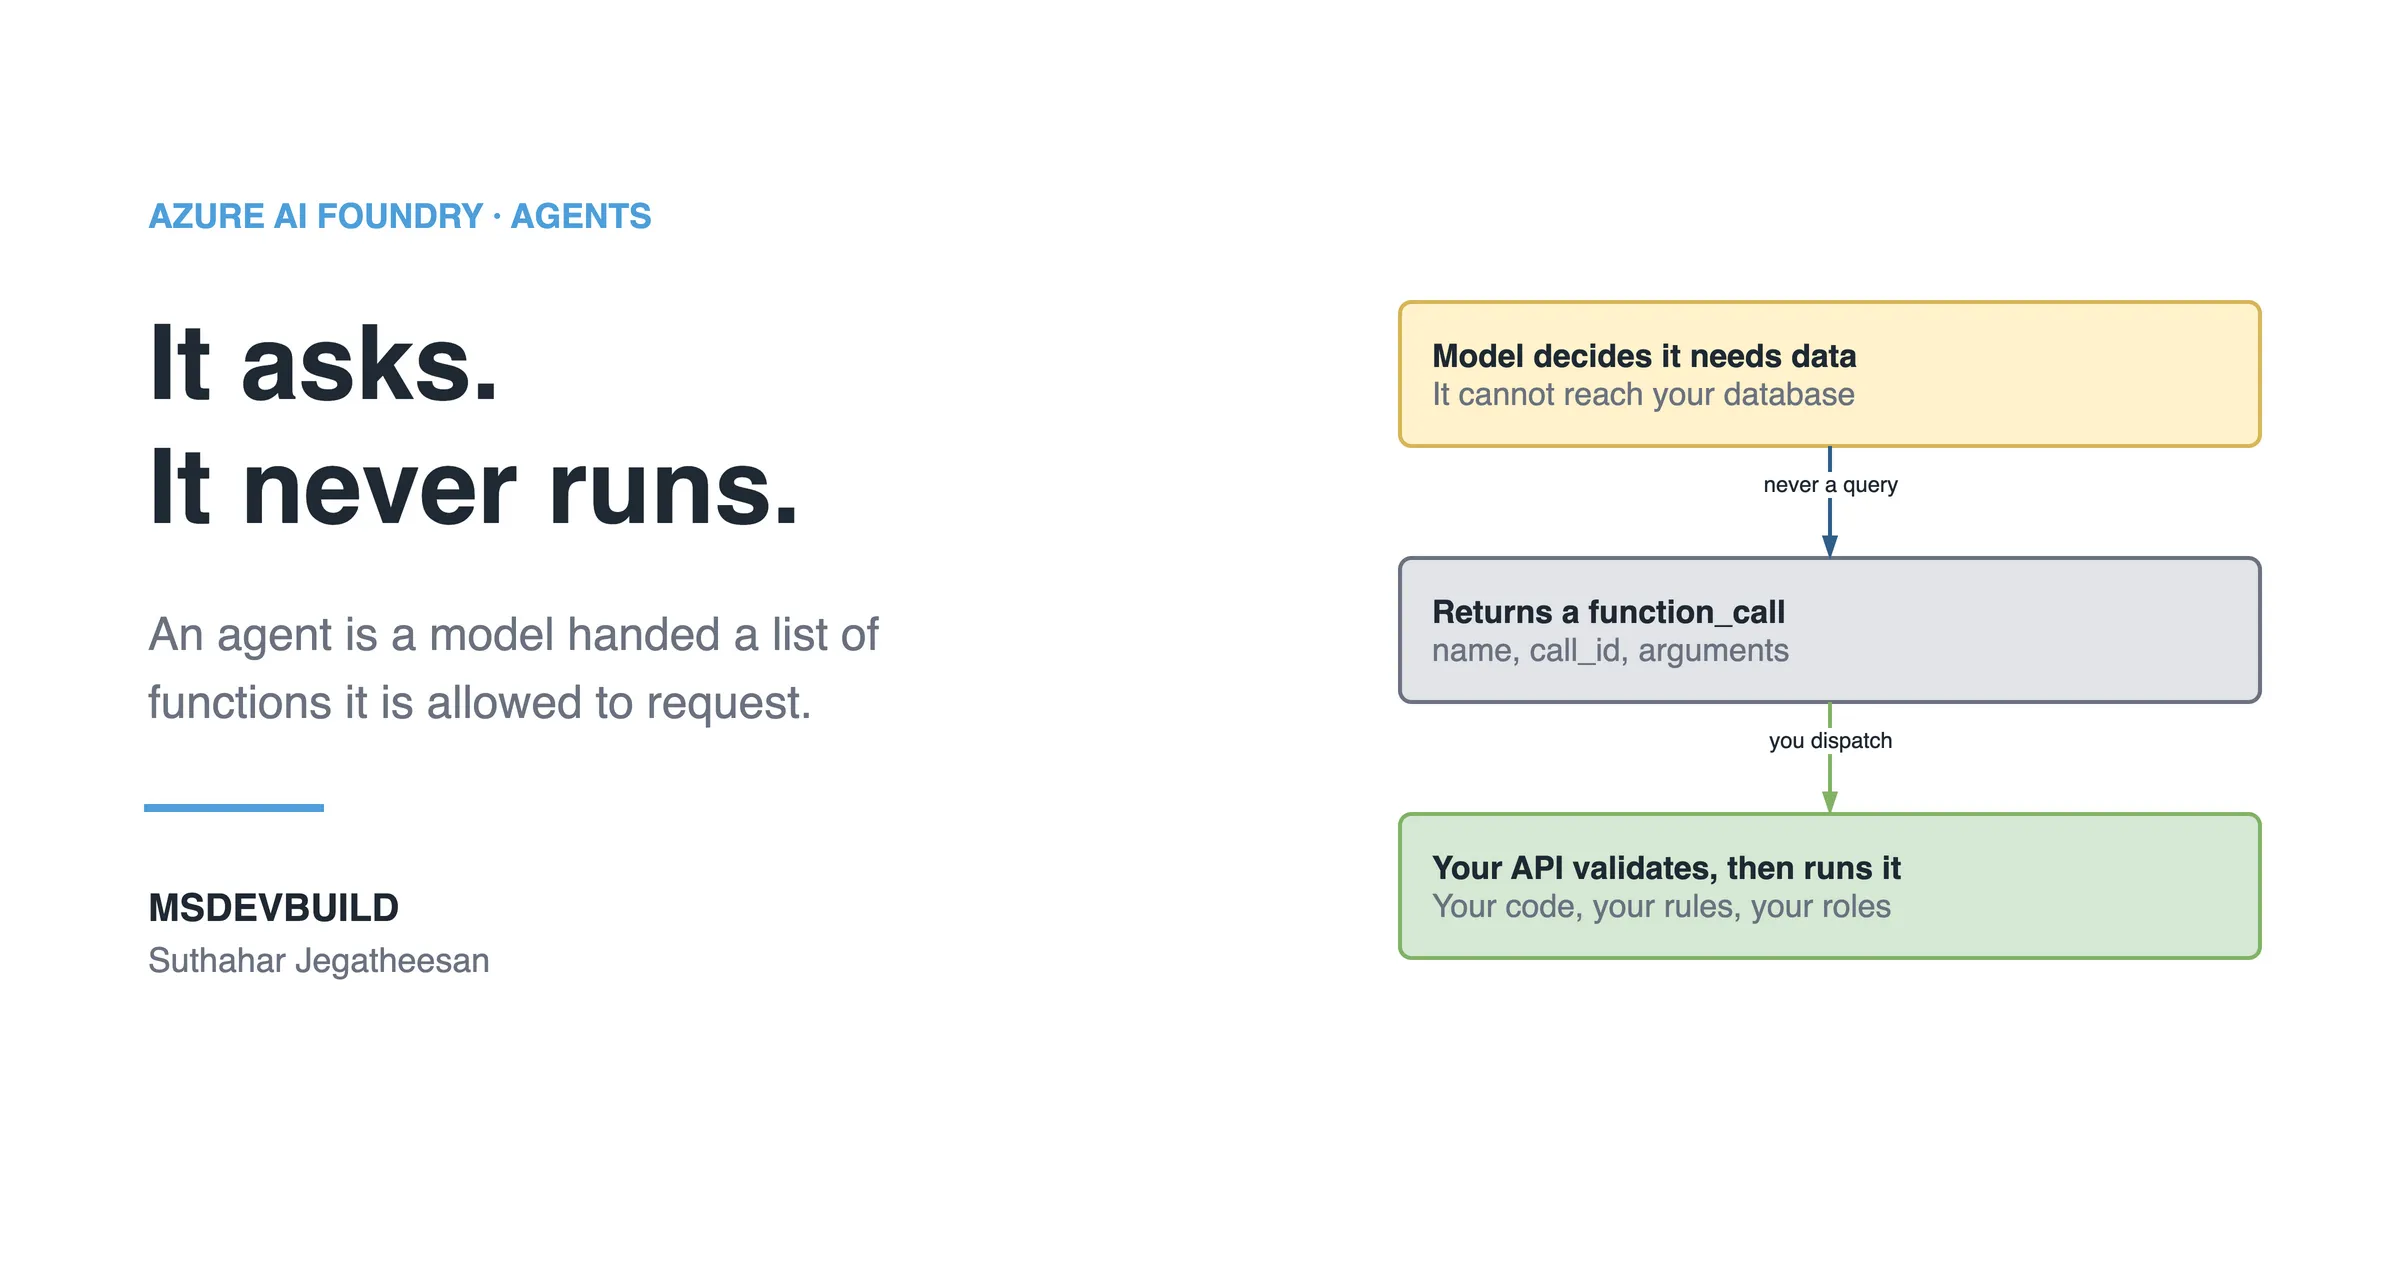
The business case for an AI agent on an app that already exists, what an agent really is, and the architecture that keeps it inside its lane.
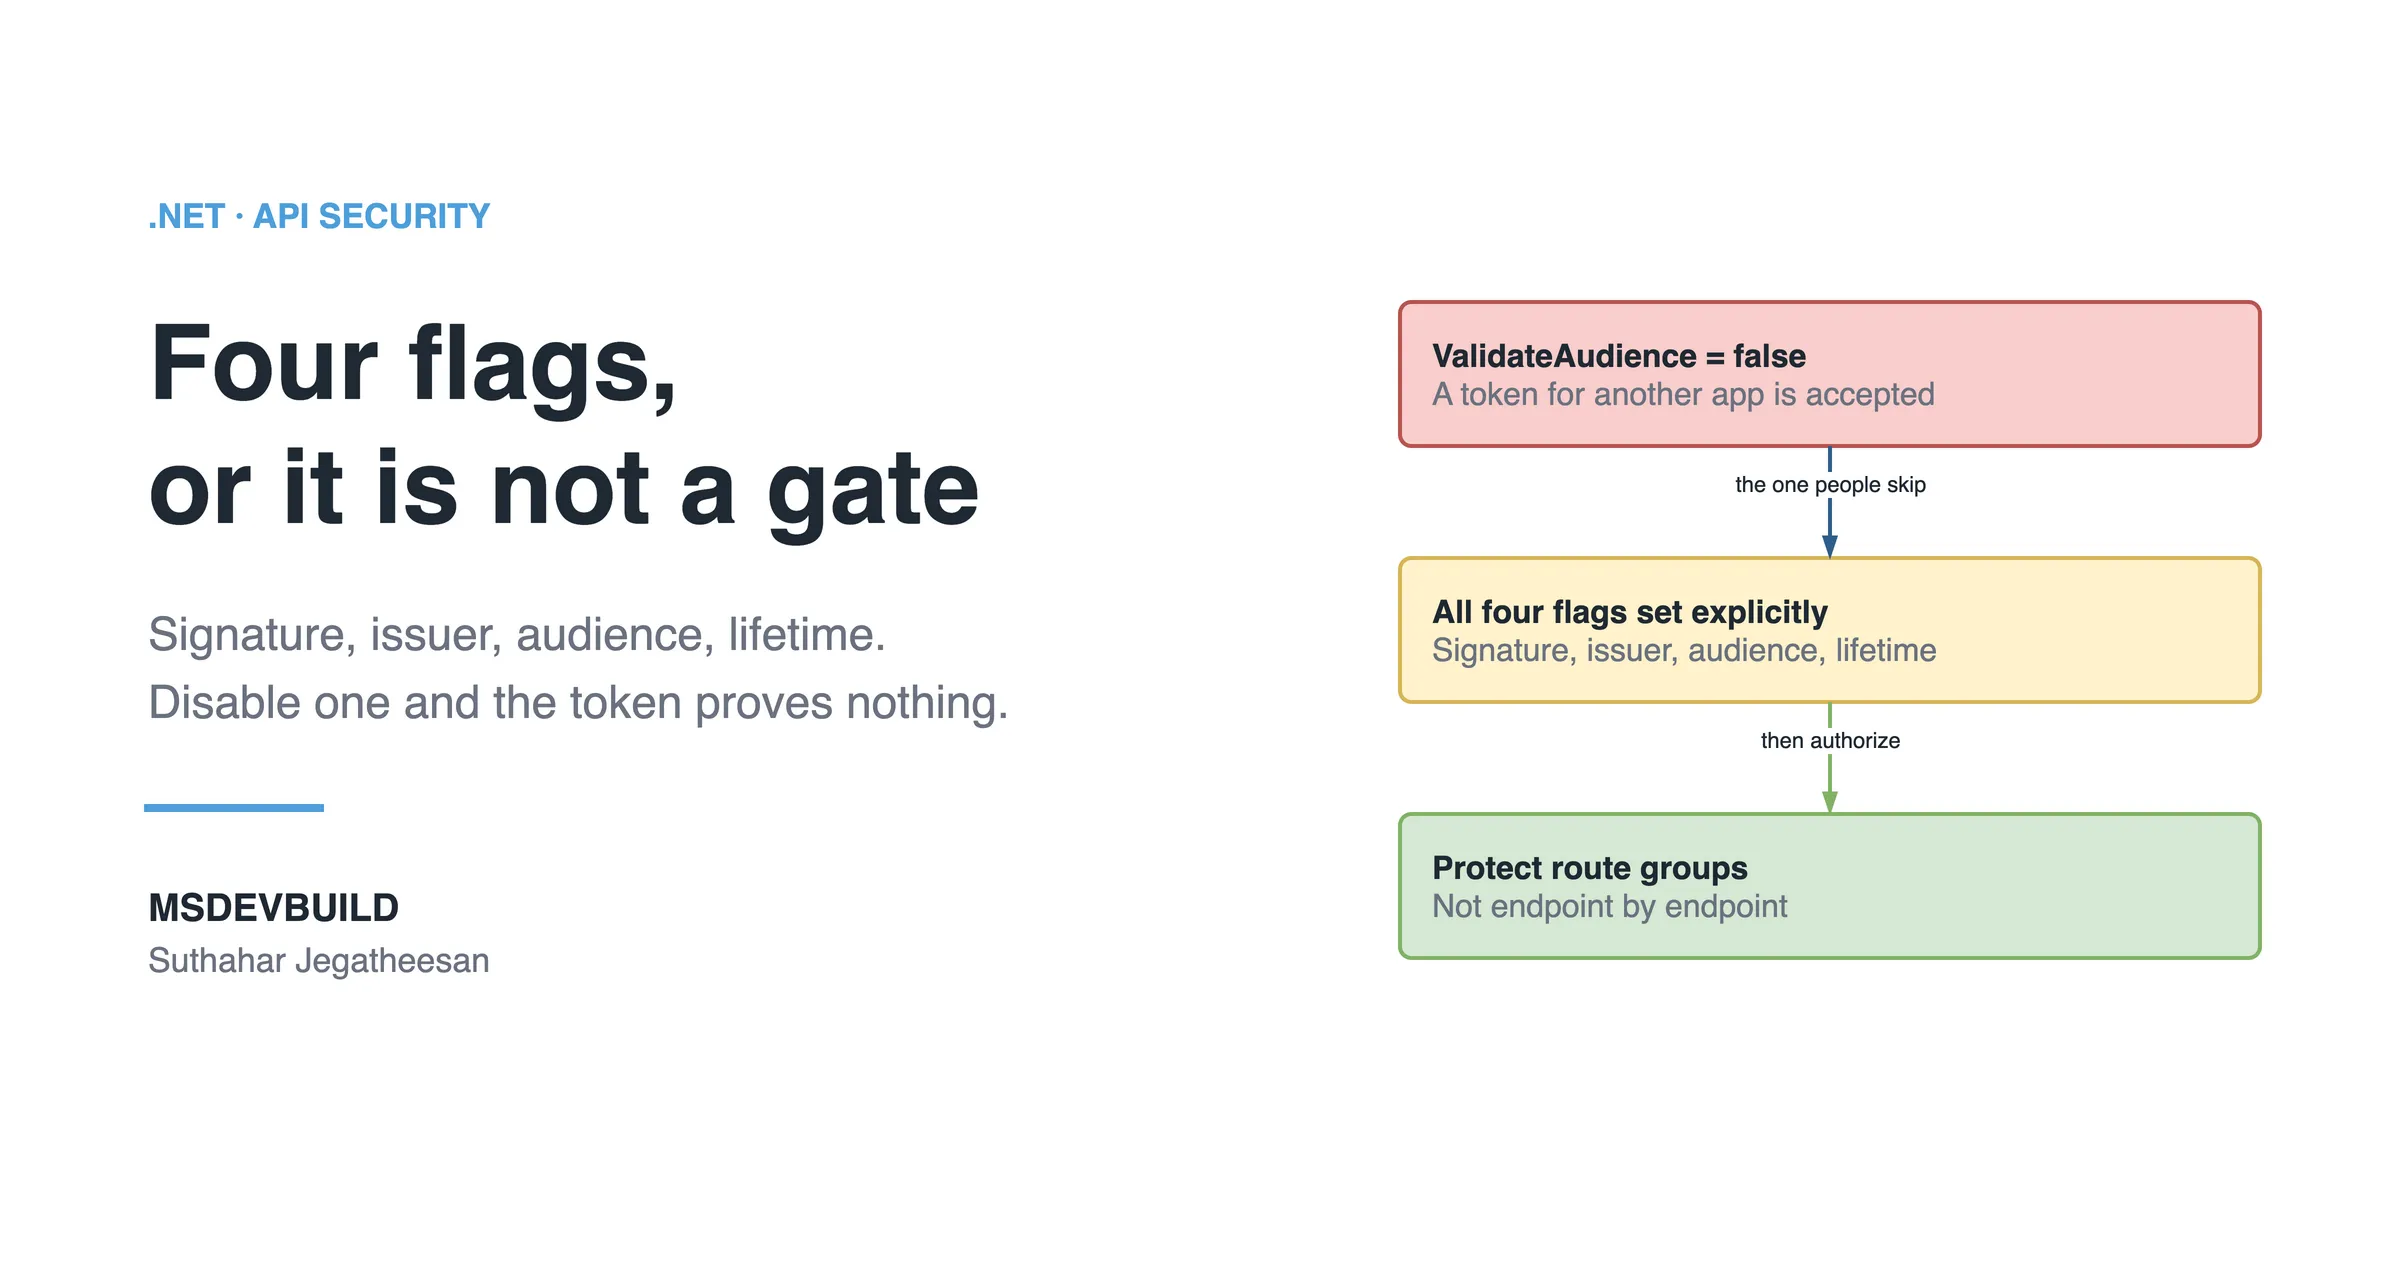
A working JWT bearer auth setup for ASP.NET Core Minimal APIs — token validation, role policies, and the config mistakes that silently disable security.
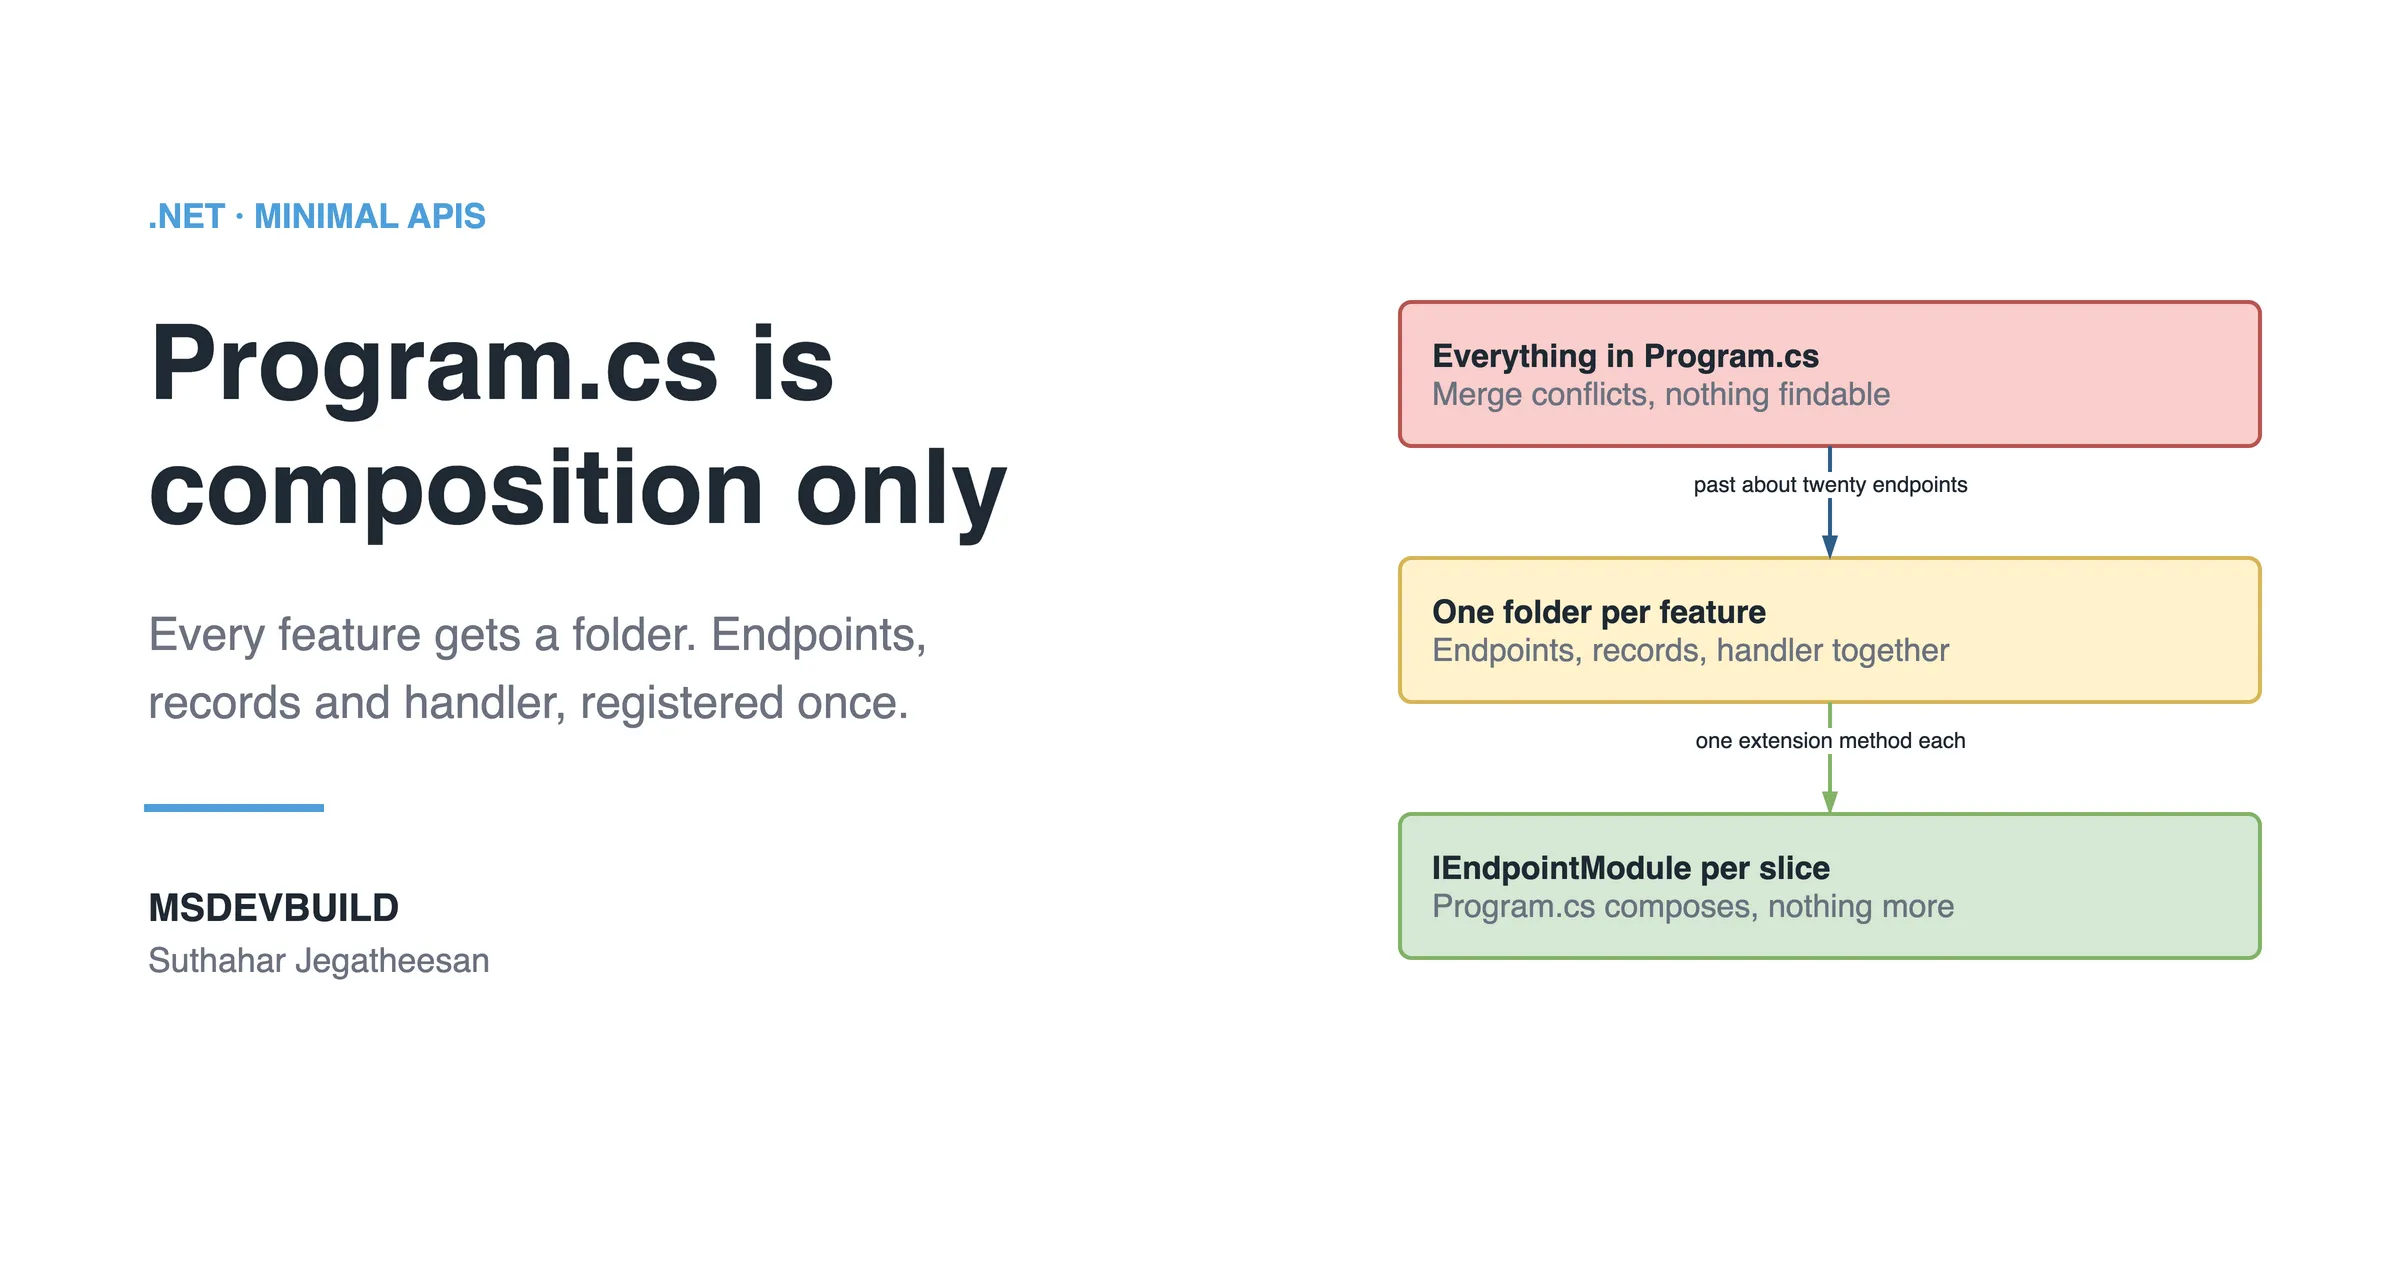
Program.cs stops scaling around twenty endpoints. Here is a vertical-slice layout for Minimal APIs that keeps routing, validation and handlers organised.
New technical articles, Azure AI and GitHub Copilot updates, and upcoming events. No spam, unsubscribe anytime.
Apple only allows adding an app from Safari. Three quick taps:
You're not in Safari right now. Open blog.msdevbuild.com in Safari, then follow these steps.