AI Bot Attacks on a Mobile App Login, and How Azure Stops Them
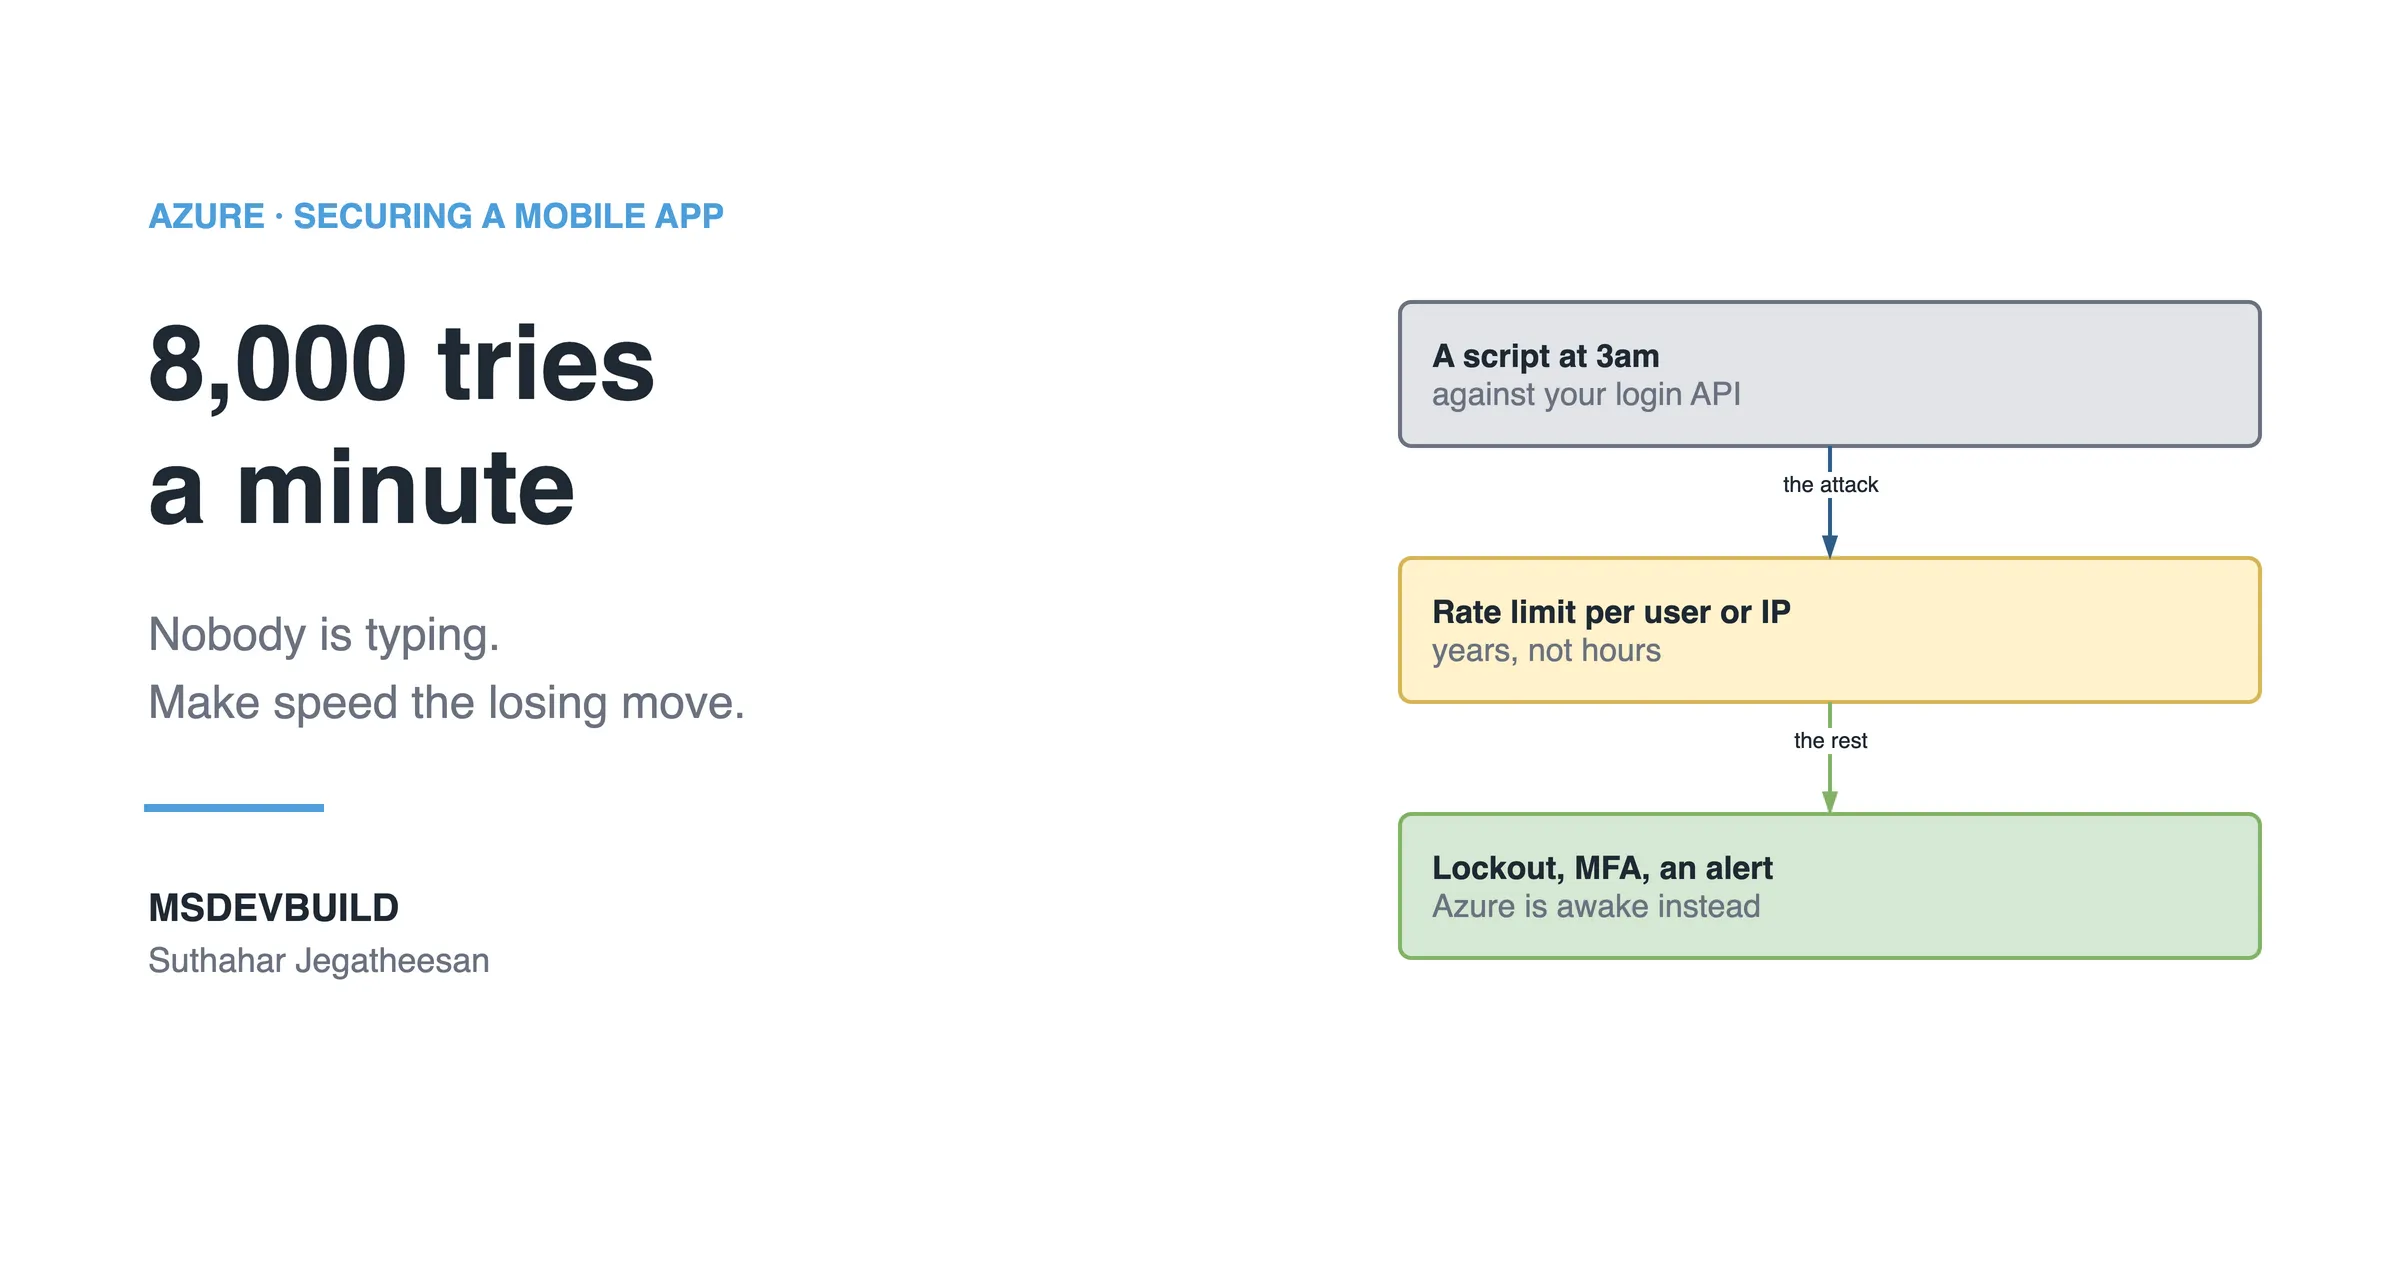
A script tries 8,000 passwords a minute against your login API at 3am. Rate limiting, smart lockout and Defender for Cloud make speed the losing move.
9 articles
A script tries 8,000 passwords a minute against your login API at 3am. Rate limiting, smart lockout and Defender for Cloud make speed the losing move.
Moving every secret into Key Vault leaves exactly one behind: the credential that opens the vault. A managed identity is what removes it.
HTTPS only, authentication, authorization, secrets and monitoring: five steps to secure a mobile API on Azure, and why the order carries most of the value.
Five findings on a working mobile app, none deliberate: a secret in the package, a token in plain storage, an open endpoint, TLS off, extra permissions.
Five common attacks on one Azure mobile backend and the control that stops each: WAF, Entra ID, an owner check, Key Vault and a private endpoint.
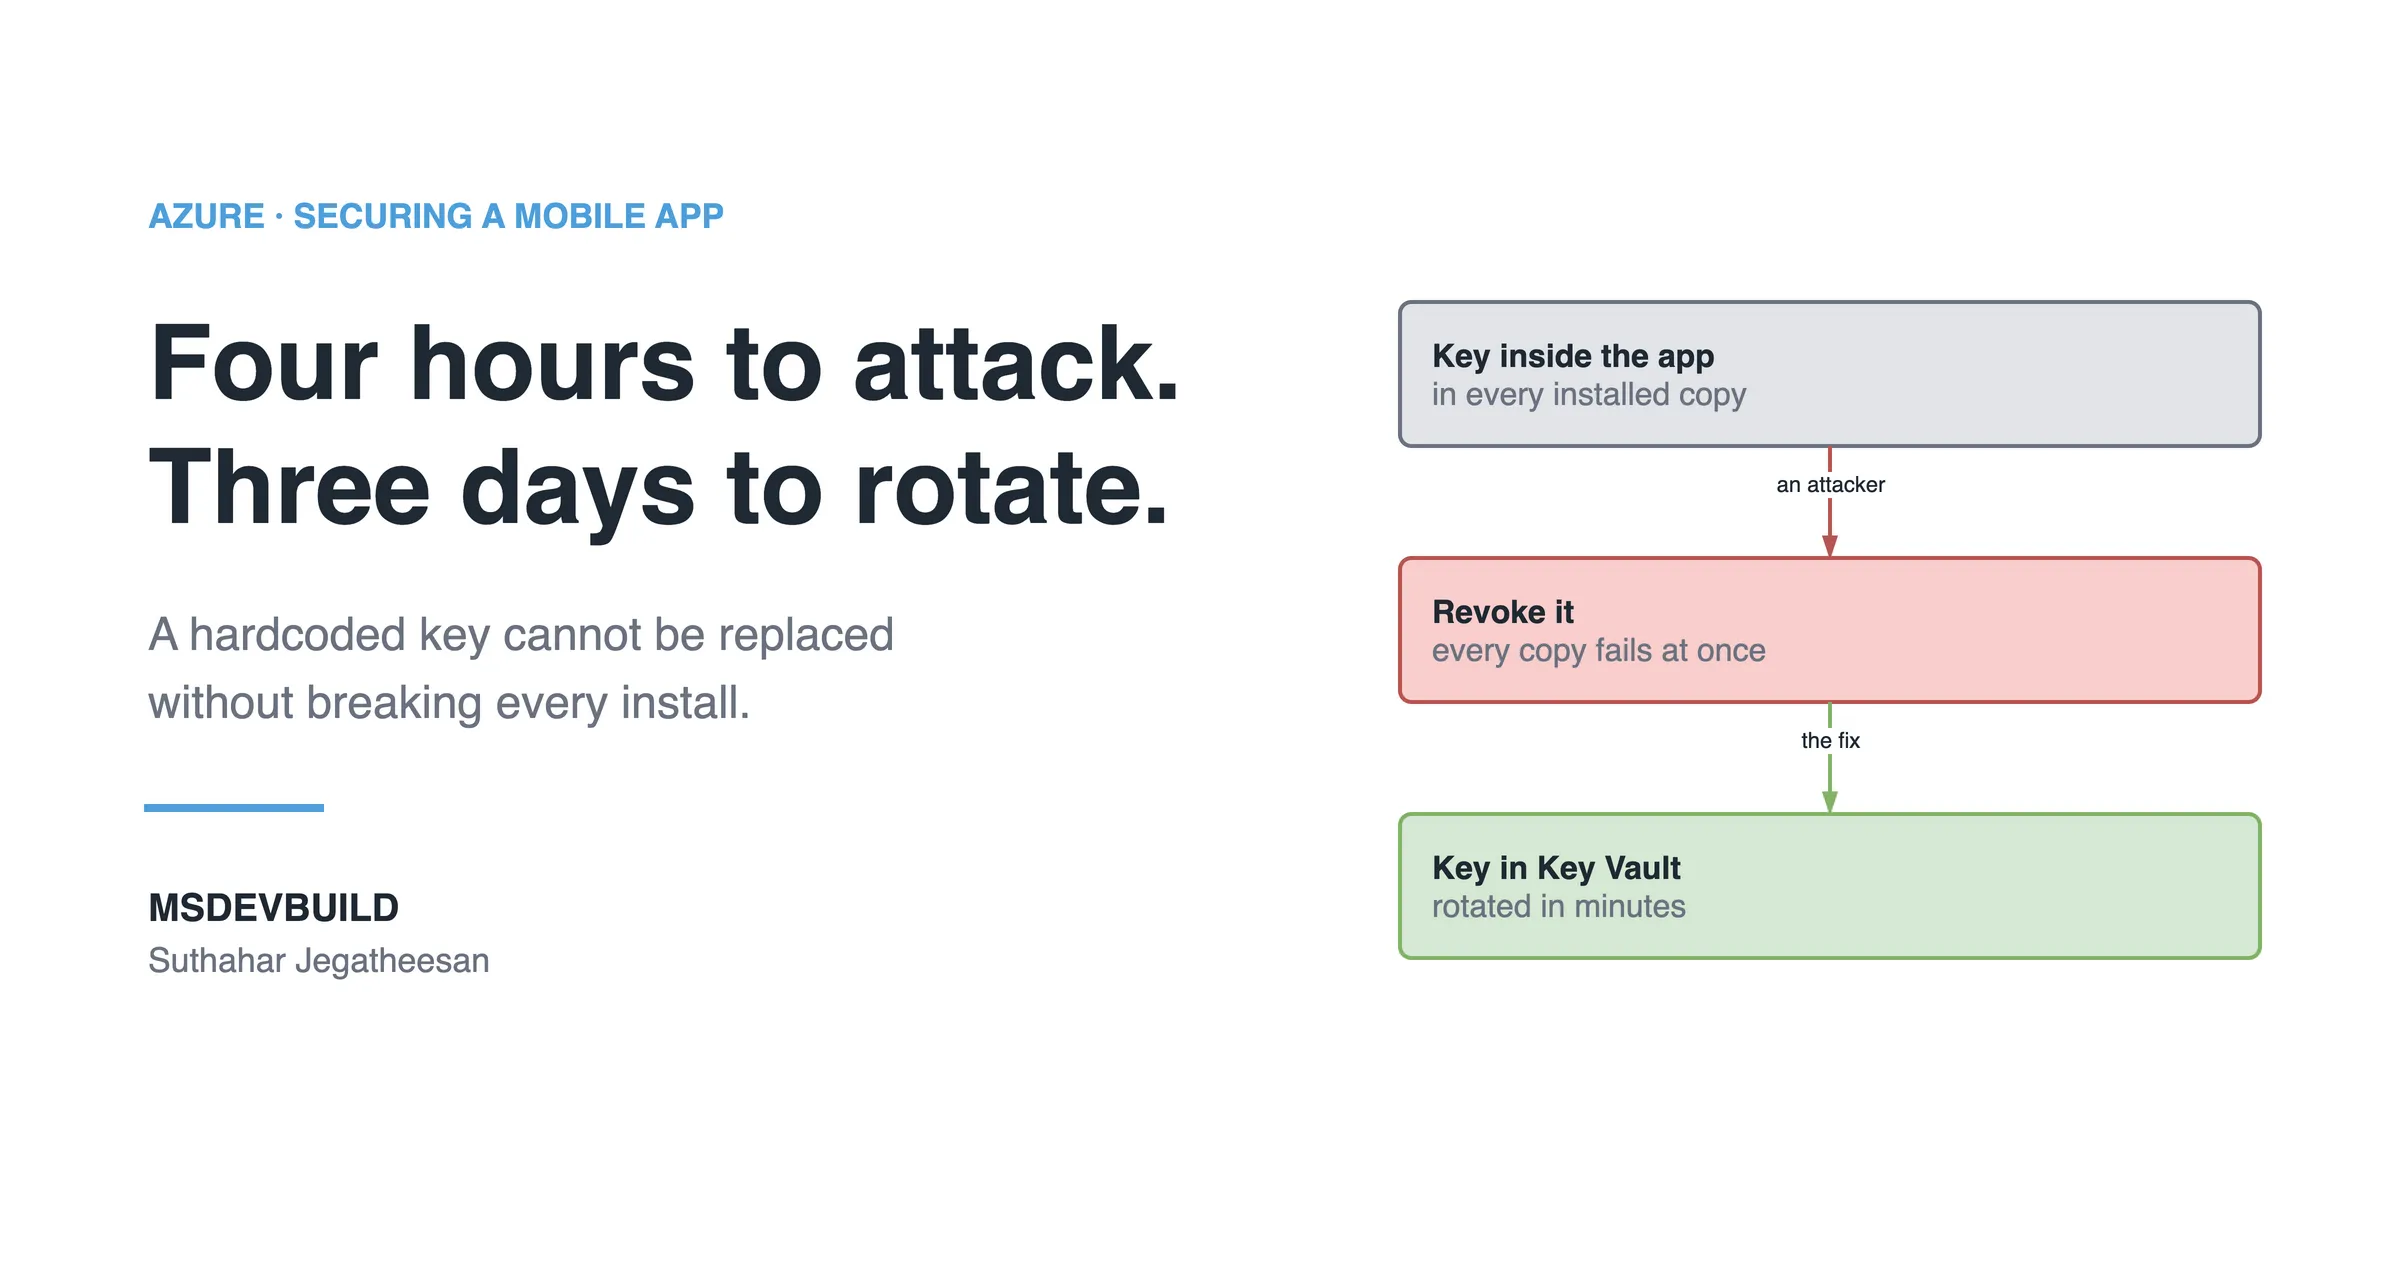
The attacker costs you hours. Rotating a key baked into 40,000 installed apps costs you days, and that gap is the real price of a hardcoded secret.
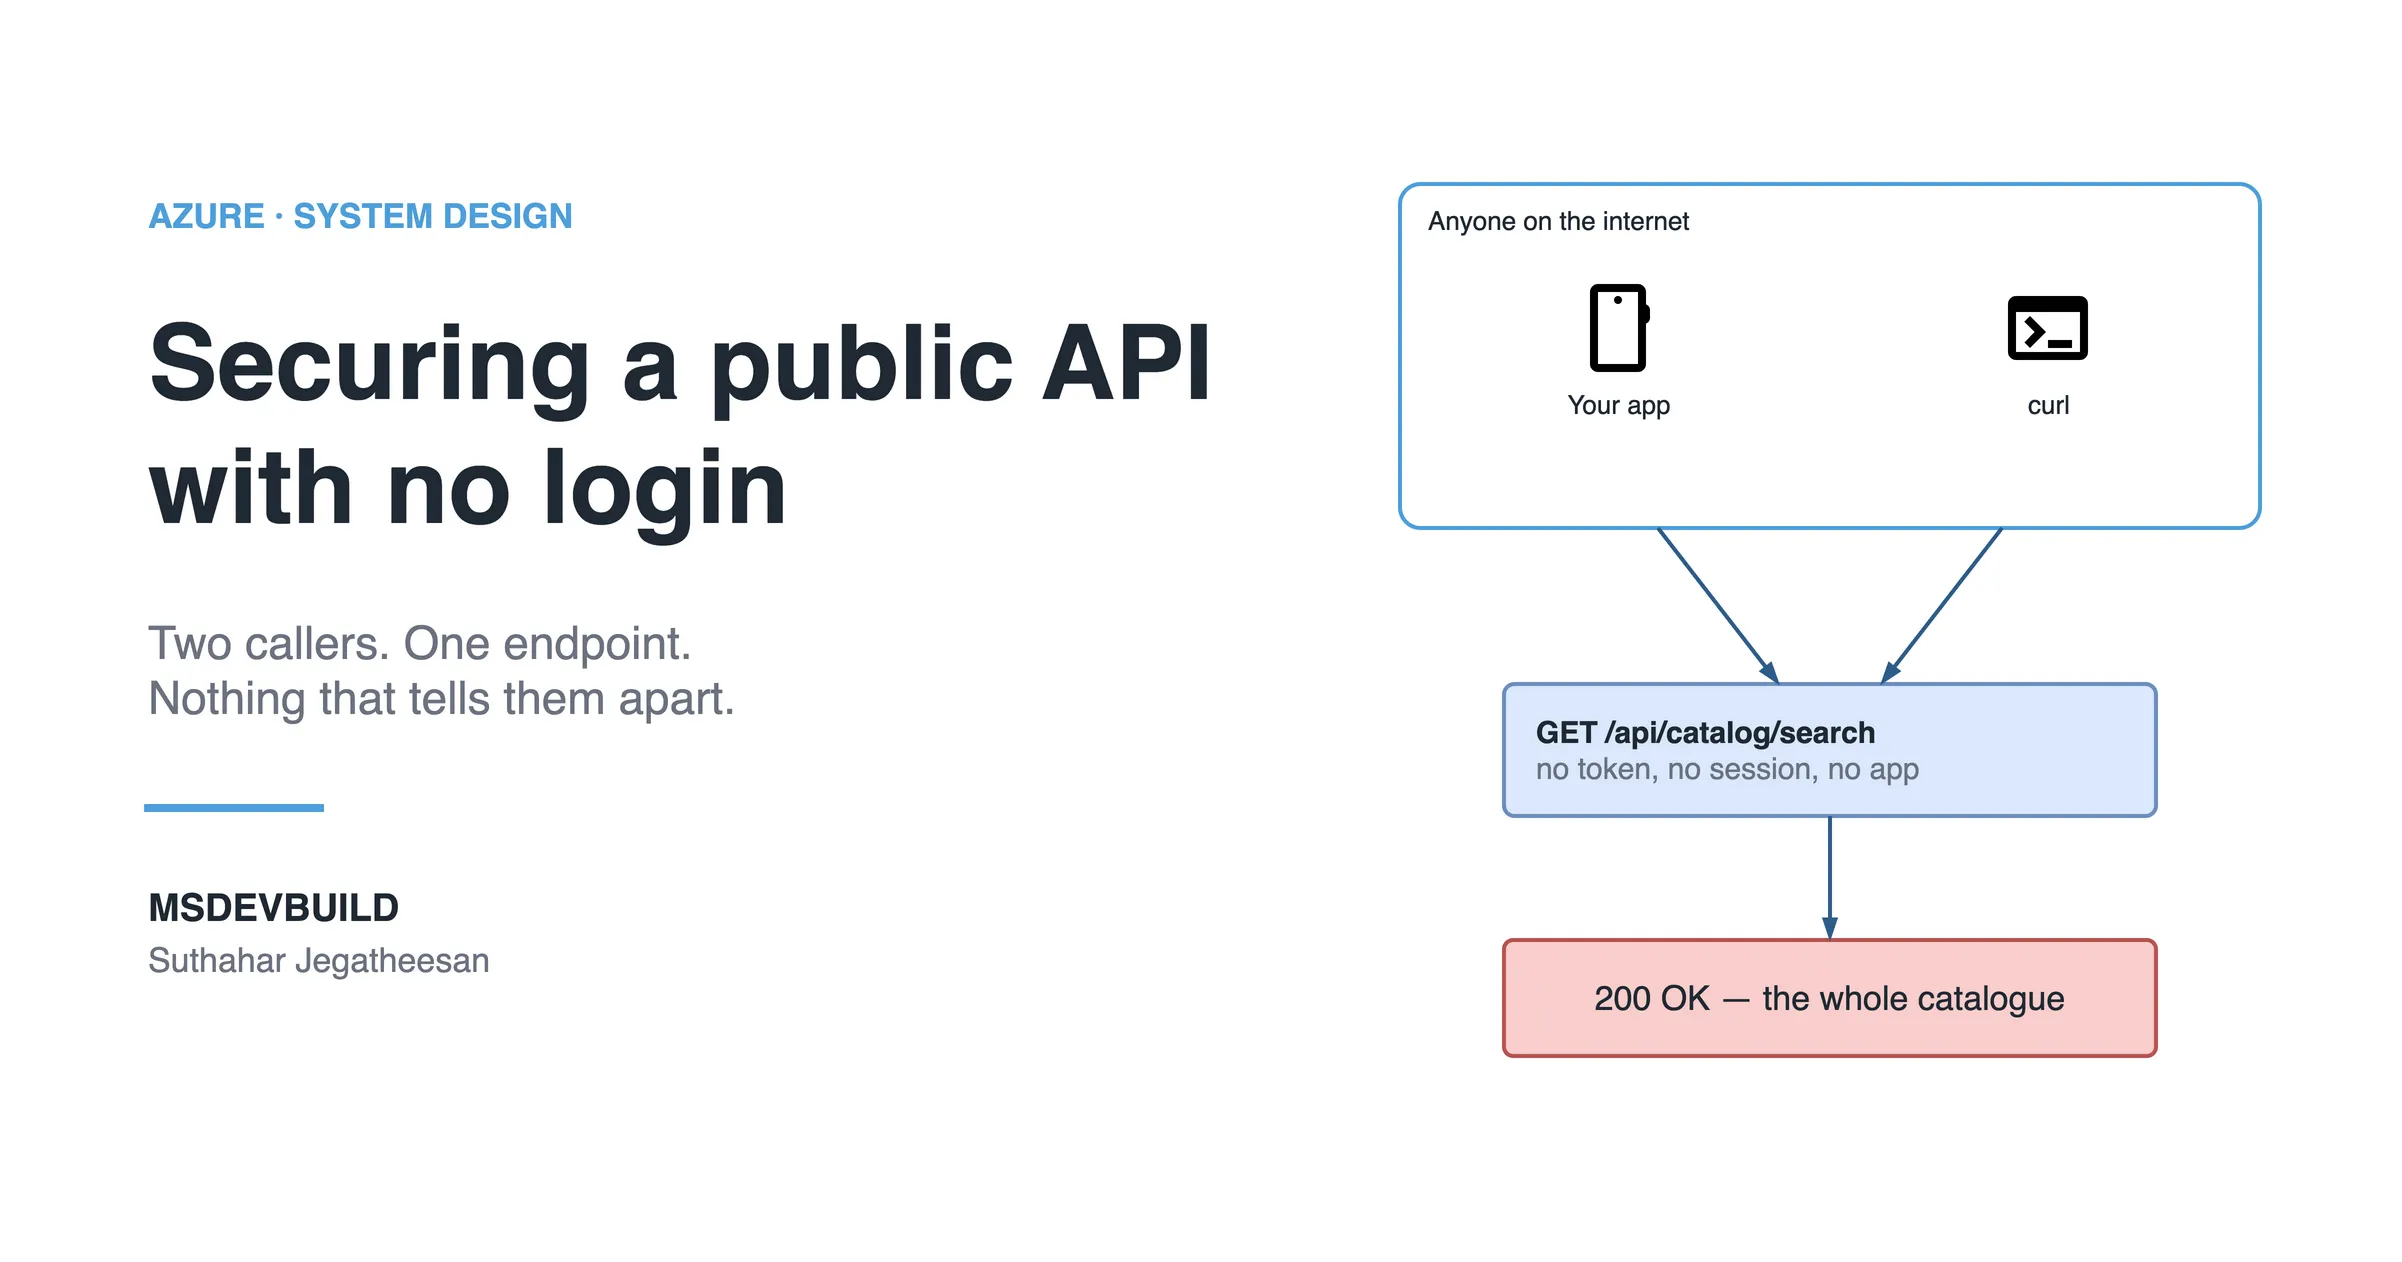
Browsing products without login was a real requirement. Trusting requests because they came from our own app was the bug, and curl does not care.
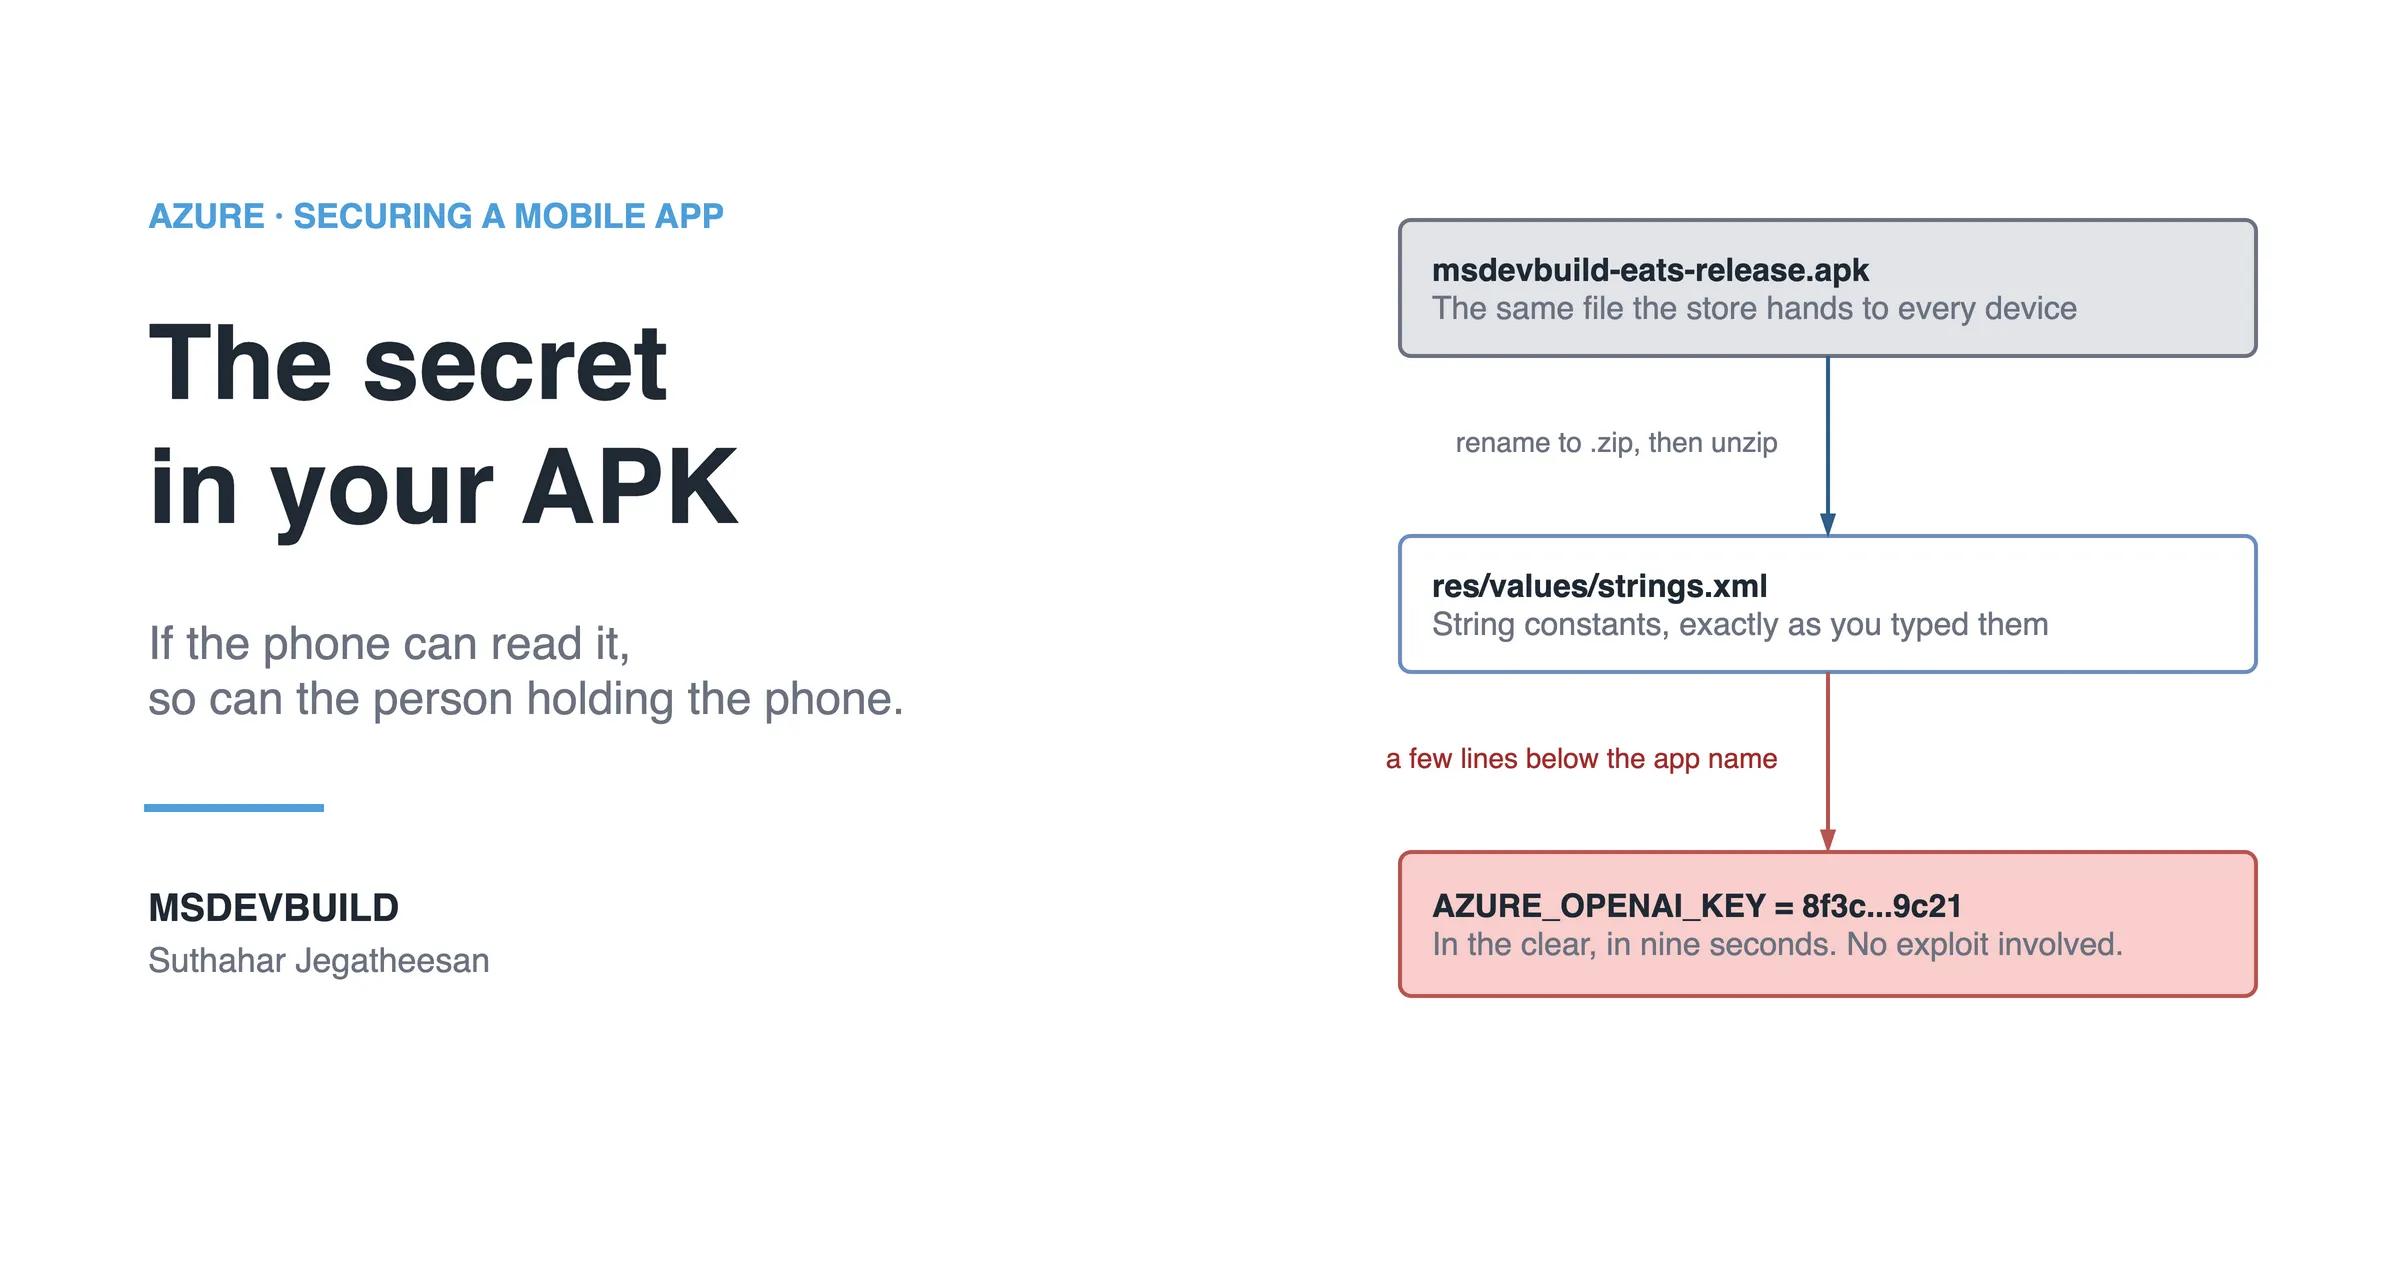
An APK or IPA is a zip file. Anything hardcoded inside it, including your API key, is already public — and here is how to get it off the phone for good.
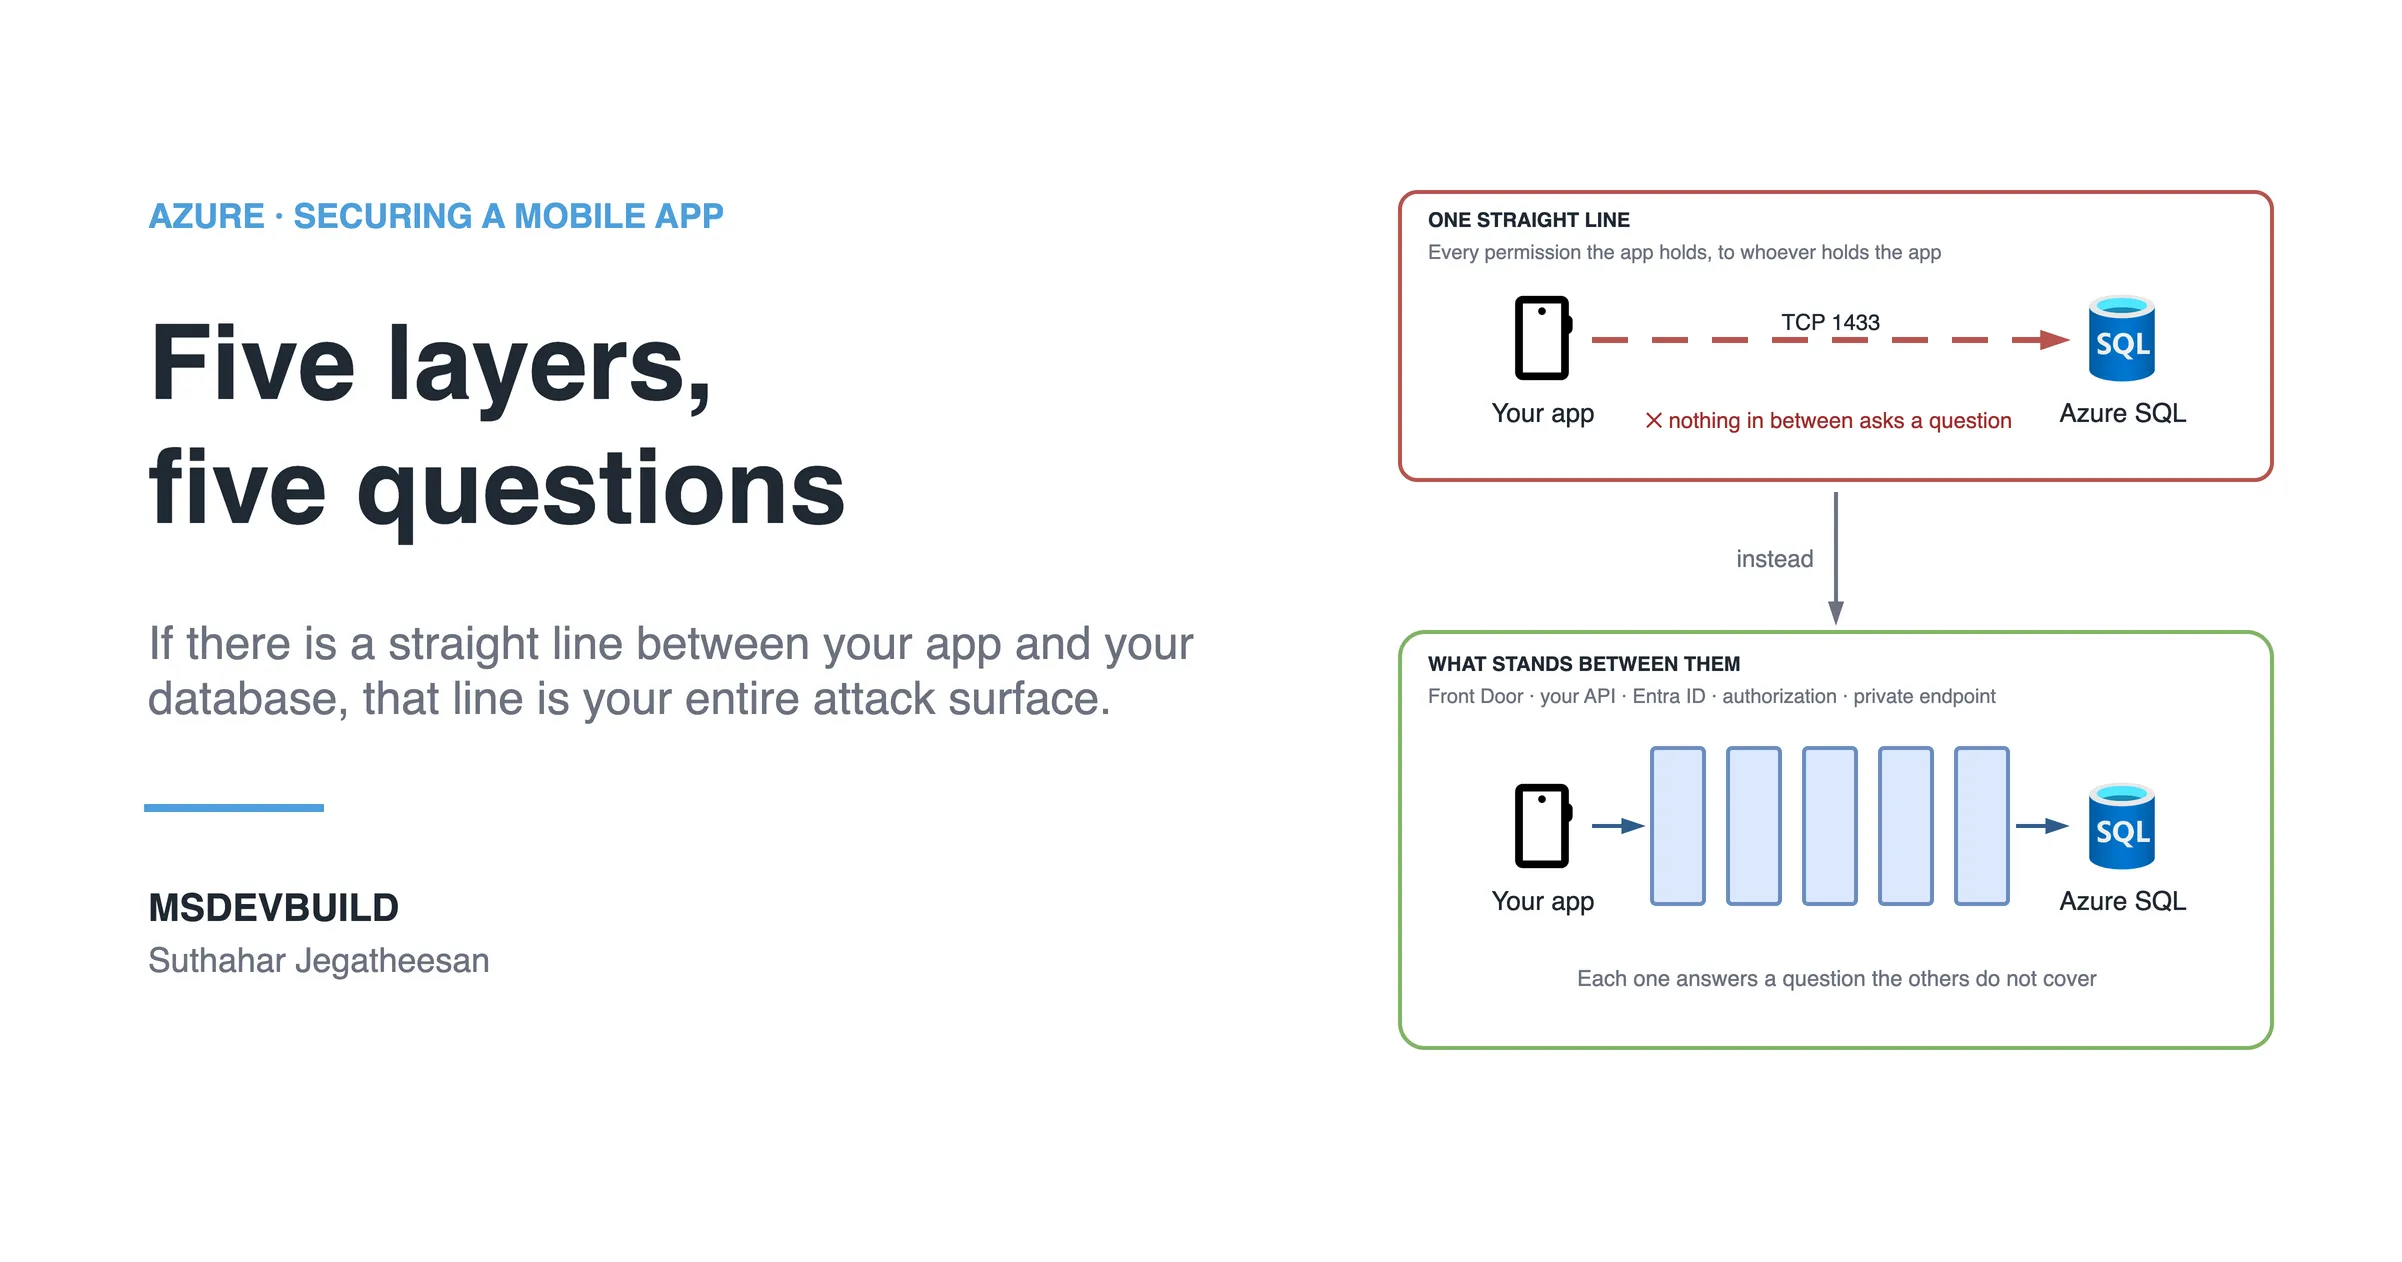
Front Door, your API, Microsoft Entra ID, authorization and a private database — the five layers that stand between a mobile app and its data on Azure.
New technical articles, Azure AI and GitHub Copilot updates, and upcoming events. No spam, unsubscribe anytime.
Apple only allows adding an app from Safari. Three quick taps:
You're not in Safari right now. Open blog.msdevbuild.com in Safari, then follow these steps.